Acedra
A cloud-native student information and document vault for institutions.

- Python 3.12 · Terraform · Shell
- PostgreSQL on Amazon RDS, private subnet
- ap-south-1 (Mumbai)
- MIT
Problem
Academic institutions need student records and documents kept strictly apart by role, with secrets out of the codebase. Acedra is a REST backend for student information and document management built for universities, departments and faculties.
Features
- Modular REST routes across authentication, students, departments and documents.
- Role-based access control with strict separation between admin and student roles; a student reaching for another student's record or file gets 403.
- A secure document vault: files stream to a private S3 bucket and are downloaded only through presigned URLs that expire after 300 seconds.
- Zero hardcoded secrets: a local .env in development and AWS Secrets Manager in production.
- Relational integrity on PostgreSQL 16 through SQLAlchemy 2.0, with reversible Alembic migrations.
- Interactive OpenAPI 3.0 documentation at /docs and /redoc.
Design decisions
- A one-to-one link from user to student profile, and departments that own students; deletions of a department are guarded by enrolment.
- JWT (HS256) authentication with bcrypt password hashing; ownership is enforced at the service level, not just in the router.
- Uploads are capped at 10 MB and never leave a private bucket; nothing in S3 is reachable without a short-lived signed URL.
- Pydantic v2 validation and SQLAlchemy parameterised queries keep input sanitised and SQL injection out.
- The test suite runs against an in-memory SQLite database with S3 fully mocked, so CI needs no AWS account.
- A multi-stage Dockerfile runs the app as an unprivileged user; GitHub Actions publishes to ECR keylessly through OIDC on every push to main.
Architecture
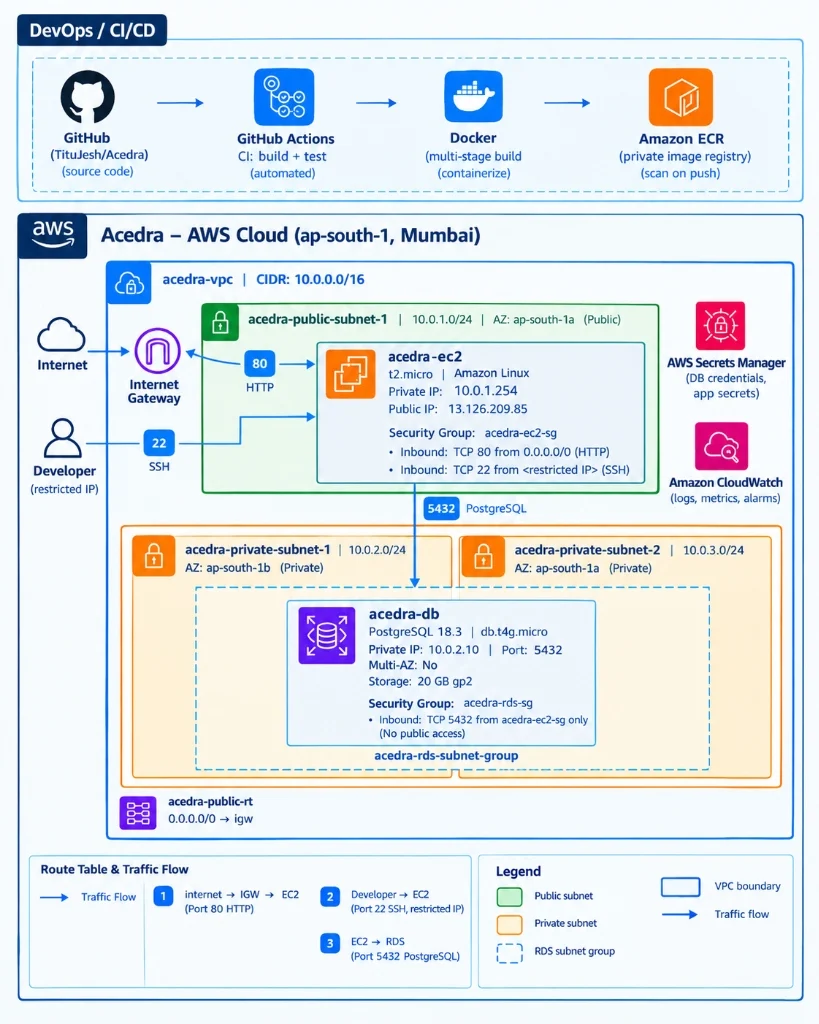
- GitHub Actions → ECR
- EC2 (public subnet)
- RDS PostgreSQL (private subnet)
- Amazon S3
- AWS Secrets Manager
- CloudWatch
Tech stack
- Python 3.12, FastAPI, Pydantic v2, Uvicorn and Gunicorn
- PostgreSQL 16, Psycopg 3, SQLAlchemy 2.0, Alembic
- S3 (boto3), Secrets Manager, JWT (HS256), bcrypt
- Docker, Amazon ECR, GitHub Actions (OIDC), Terraform, CloudFormation
API
/auth/register · /auth/loginRegistration and JWT issue; /auth/me for identity/students/ · /students/me · /students/searchDirectory with dept, year and gender filters; admin write/departments/Department catalogue, enrolment-guarded deletes/documents/upload/{id}Private S3 upload, 10 MB limit; download via a 300 s signed URL
Result
Student and admin data are kept strictly apart, every document URL expires in five minutes, and the schema can be migrated forward and back without manual SQL. The whole stack deploys to ap-south-1 from Terraform or CloudFormation.