CloudExpire
Temporary AWS resources that clean up after themselves.
- Python 3.12 · Terraform (HCL)
- GitHub Actions CI
- ap-south-1 (Mumbai)
- Dry run, destruction off
Problem
Temporary cloud environments outlive their purpose, creating unnecessary cost and a wider security surface. CloudExpire is a serverless lifecycle engine: it provisions short-lived EC2 instances with a time to live of 1 to 24 hours, tracks the expiry state in DynamoDB and terminates expired resources from a scheduled Lambda.
Features
- On-demand provisioning: request an EC2 instance over a REST API with a configurable TTL of 1 to 24 hours.
- TTL tracking: DynamoDB keeps the creation timestamp, expiry window and active state of every resource.
- Automated cleanup: EventBridge triggers a cleanup Lambda every five minutes to terminate expired instances.
- Safety guardrails: destruction is disabled by default (dry run) and ownership tags are validated before any termination.
- State reconciliation: stale unprovisioned requests are recovered, and resources move through REQUESTED, ACTIVE, CLEANUP_PENDING, CLEANED or FAILED.
- Infrastructure as code: the whole AWS footprint is defined and provisioned with Terraform.
- Observability: structured execution summaries and metrics go to CloudWatch with 14-day retention.
Design decisions
- A FastAPI application behind API Gateway and Lambda handles requests; DynamoDB stores creation and expiry timestamps with the resource metadata in a single table.
- EventBridge invokes a separate cleanup Lambda every five minutes. Cleanup evaluates expiry timestamps itself instead of relying on DynamoDB TTL deletion.
- Ownership tags (Project, ManagedBy, ResourceId) are validated before any termination; EC2 launch and termination stay disabled unless enabled through explicit environment flags.
- Stale requests without an instance are marked FAILED after a grace period, so the table never fills with ghosts.
- The cleanup role restricts ec2:TerminateInstances with tag conditions; DynamoDB is on demand and the API bearer token lives in SSM Parameter Store as a SecureString.
- Terraform ignores the Lambda code hash so the cleanup package can be deployed from CI independently of the infrastructure.
Architecture
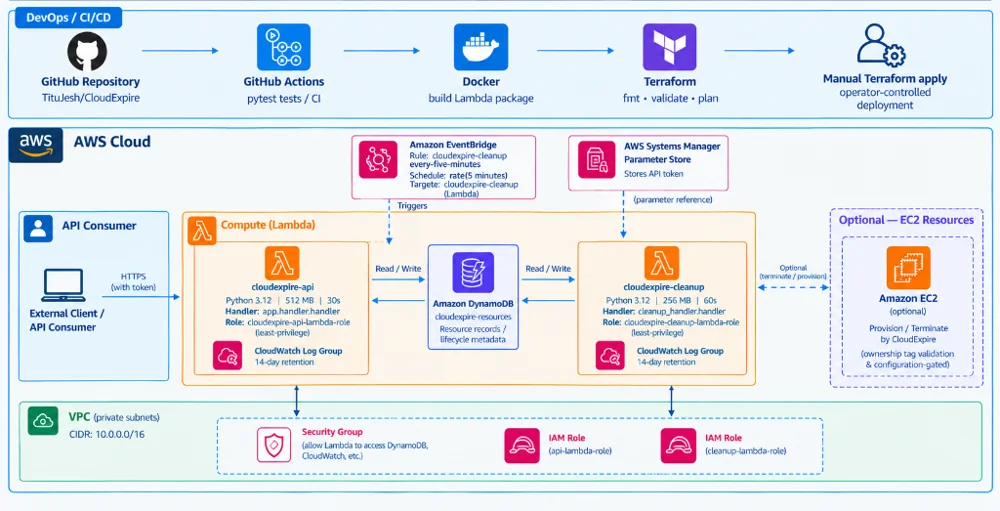
- API Gateway
- Lambda (API)
- DynamoDB
- EventBridge
- Lambda (cleanup)
- EC2
- SSM Parameter Store
- CloudWatch Logs
Tech stack
- Python 3.12, FastAPI, Pydantic v2, Uvicorn
- EC2, DynamoDB, Lambda, EventBridge, API Gateway, SSM, CloudWatch
- Terraform, Docker, pytest, GitHub Actions
API
/healthPublic service health check/resourcesRegister and provision a temporary resource/resourcesList all tracked resources/resources/{id}Resource details and lifecycle status
Result
CloudExpire automatically cleans up expired resources while checking ownership tags before termination. A planned next step is cross-account provisioning through IAM roles and STS, so users could have resources created in their own AWS accounts.